Compliance without the spreadsheet sprawl.
(FIIG, 26-021MR)
Tick what's true today.
We'll show you what changes.
Eight pains we hear every week. Tick what's true - we'll show you what the year costs in hours and dollars, and what changes with Cybereen.
Seven standards, one control library.
Create maturity-led paths
Carry your evidence across multiple frameworks
Produce board-ready presentations
See how it works
How your team will use our platform.

Triage every client from one console.
One screen for everything - branches, business units, or whole client books. Red surfaces, green stays quiet. Drill into any tenant in two clicks.
- Avg compliance, critical alerts, active remediations at a glance
- Health, tier, and "last activity" filters out of the box
- Switch into any client tenant without re-auth
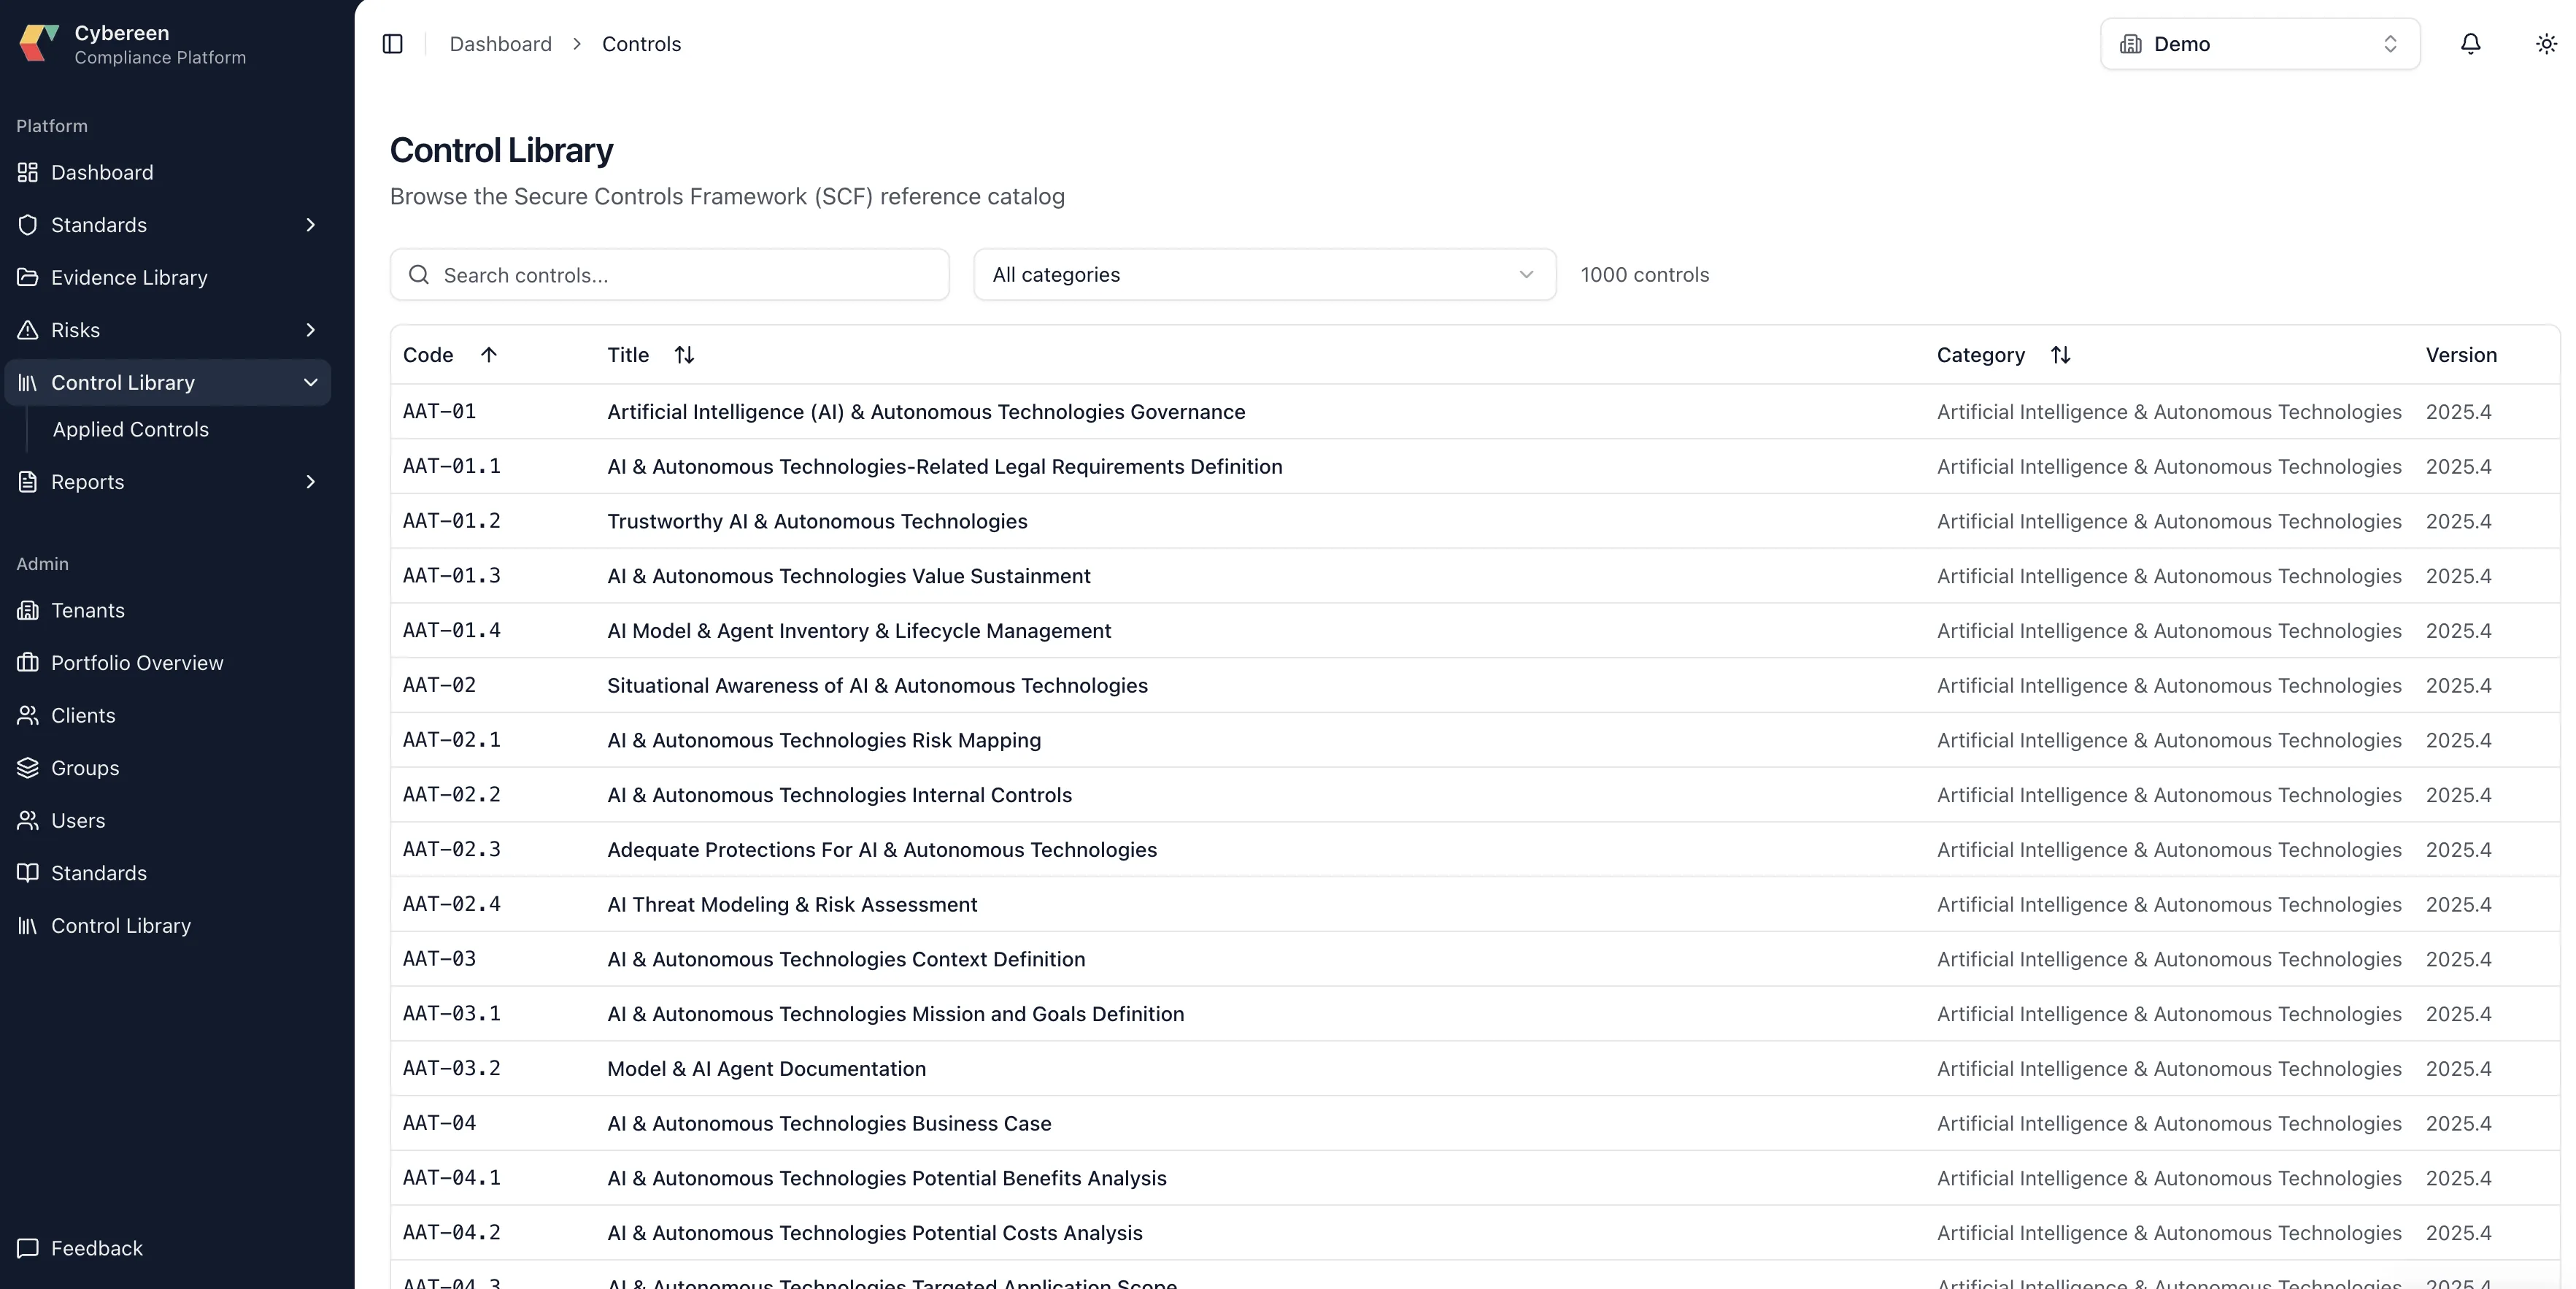
One control, many frameworks.
1,000 reference controls across 33 categories, every one mapped to the standards that share it. Answer once - ISO 27001, NIST CSF, Essential 8 all pick it up.
- SCF-aligned reference catalog, versioned and updated
- Sub-controls (e.g. AAT-01.1, AAT-01.2) for granular evidence
- Filter by code, title, category, or framework
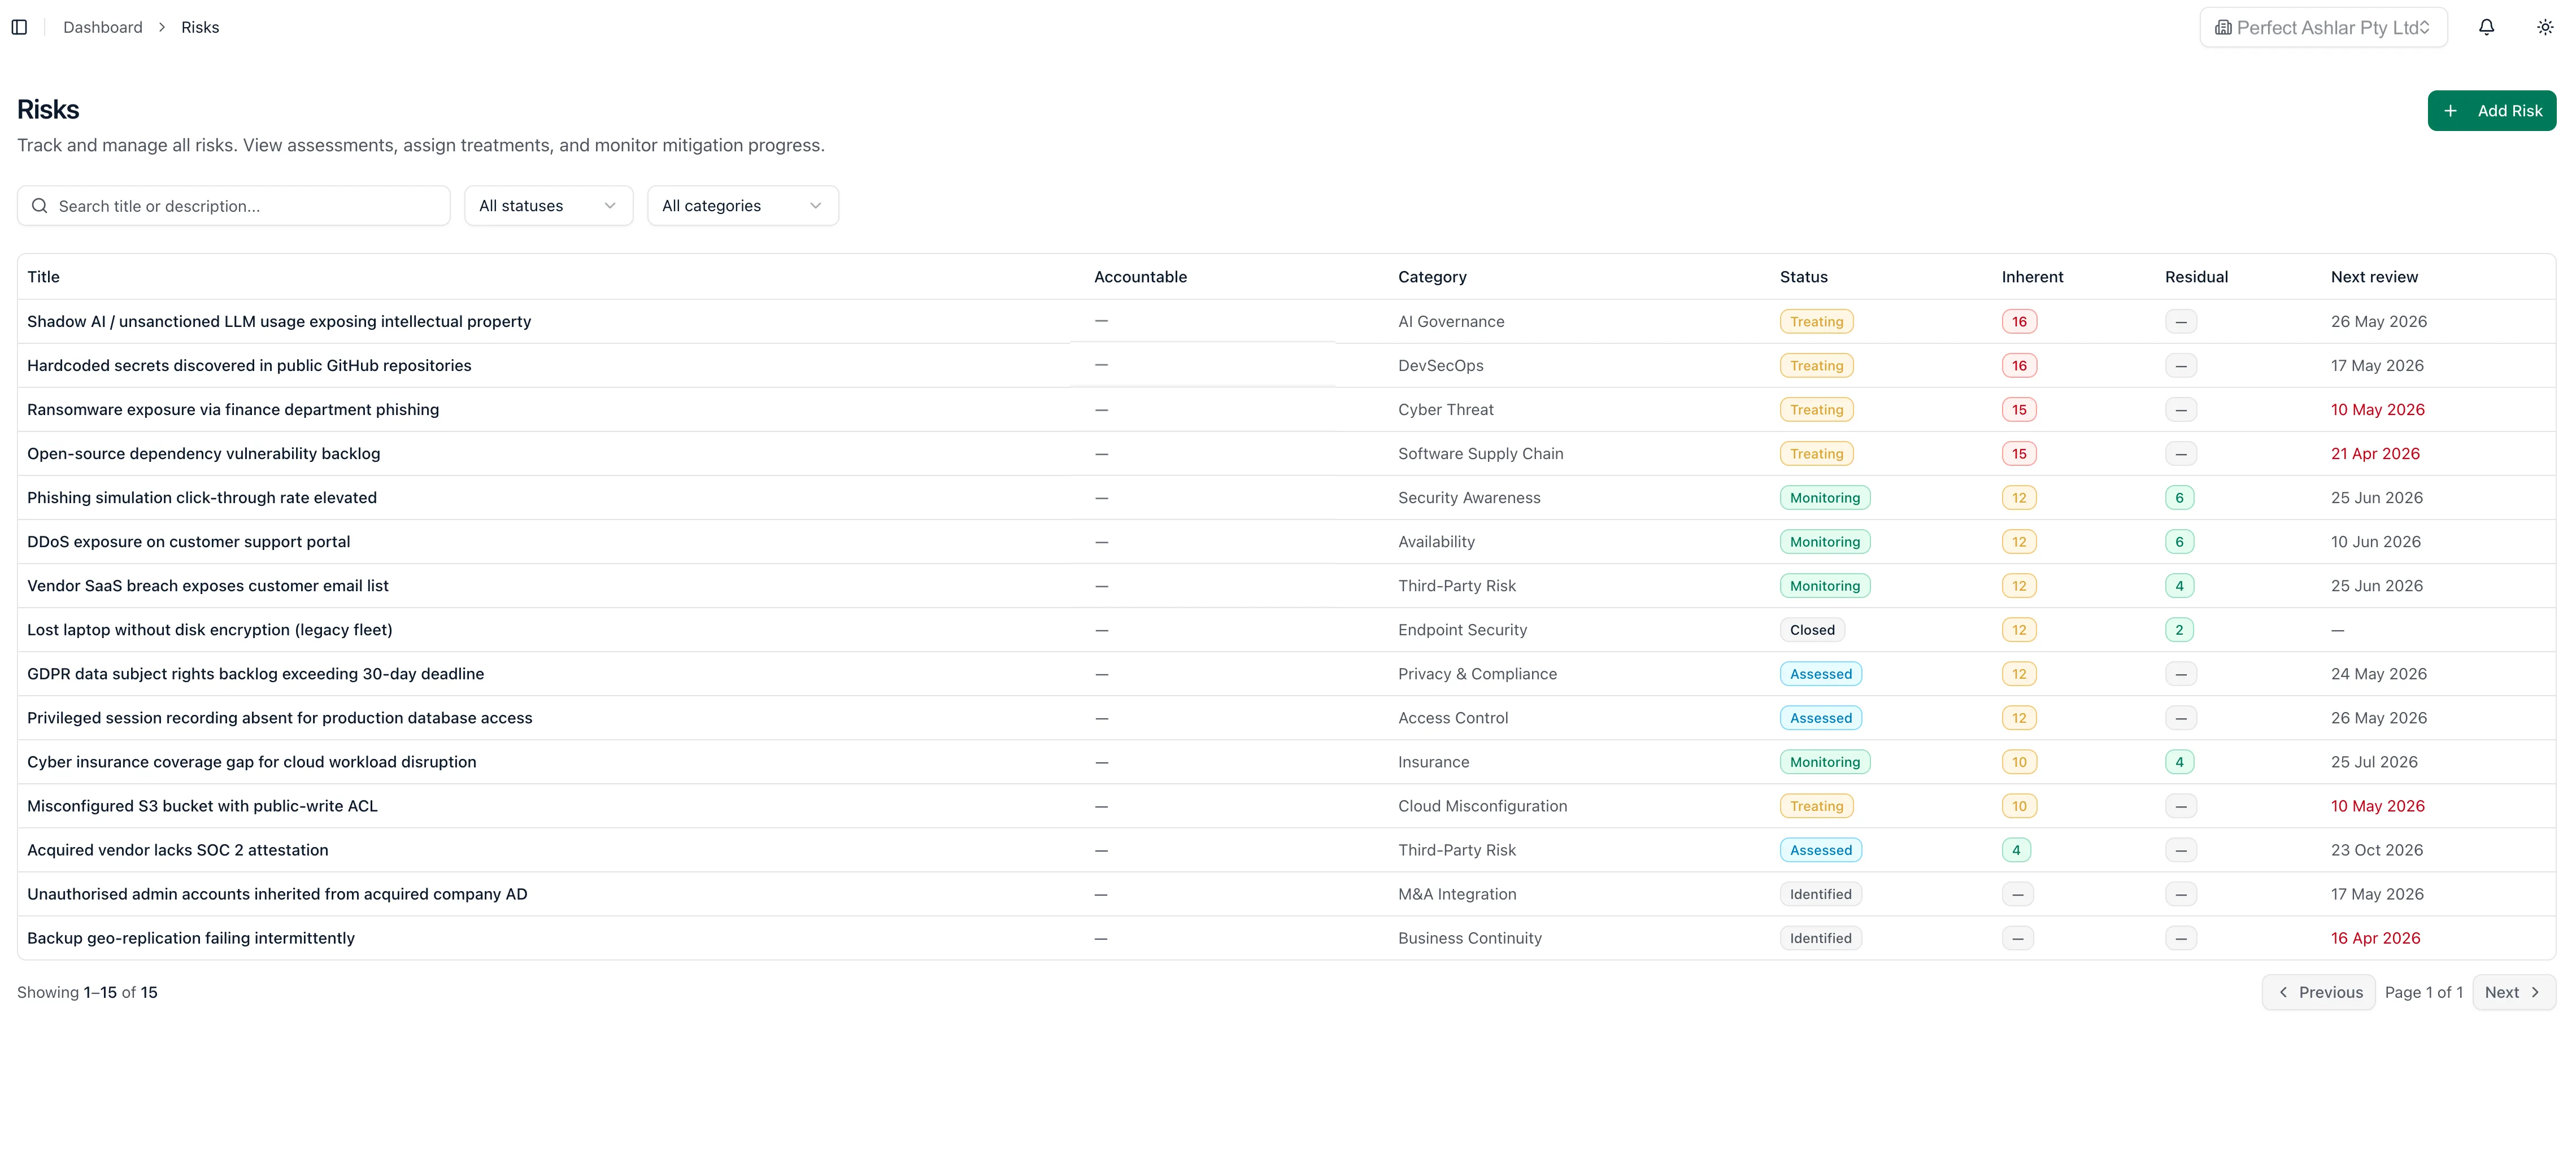
Inherent. Residual. Reviewed.
Track every risk with the numbers your auditor expects - inherent and residual scoring, treatment status, accountable owner, and the next review date. Overdue dates surface red, automatically.
- 5×5 inherent vs residual matrix, comparable side-by-side
- Treatment workflow: identified → assessed → treating → monitoring → closed
- Categories pre-seeded: AI, Cyber, Third-Party, Cloud, Privacy, M&A
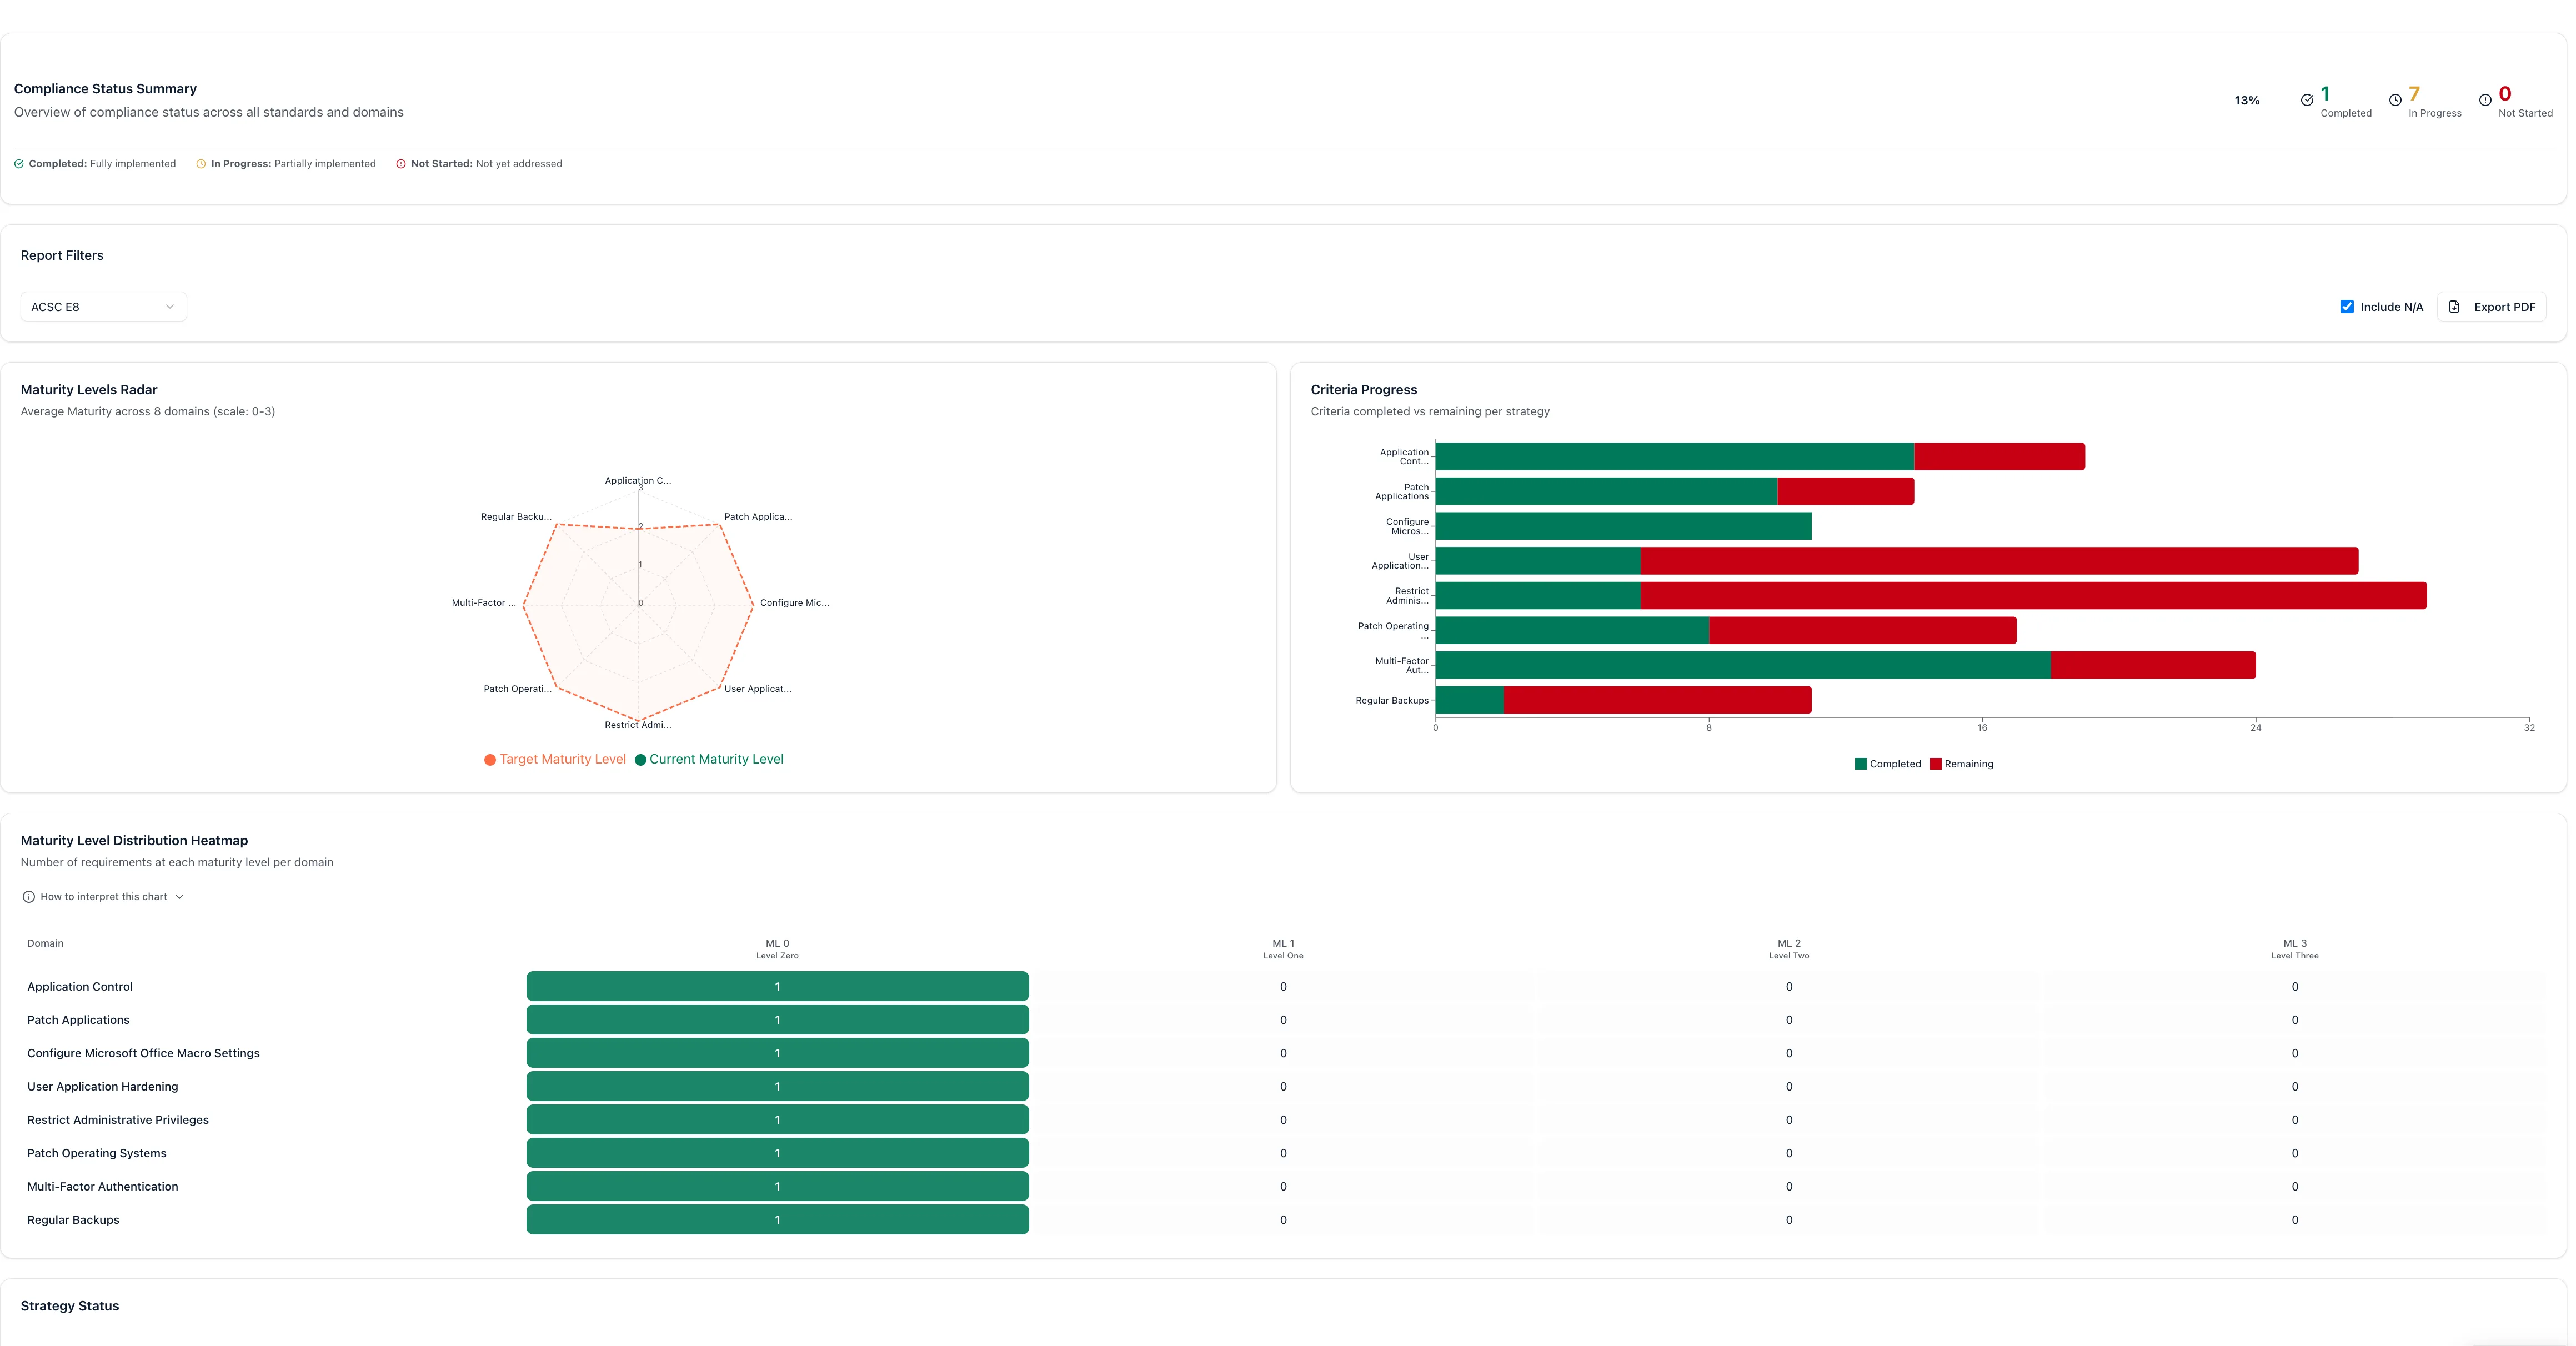
Board-ready, every time.
Maturity radar, criteria progress, and the gap to your target - generated, not hand-built. Export to PDF for the board pack; share a live link with your auditor.
- Filter by standard: Essential 8, ISO 27001, APRA, NIST CSF
- Current vs target maturity, by domain
- Criteria-progress bars per strategy, completed and remaining
Clients are NDA-bound - sector references available on request.
What's new.
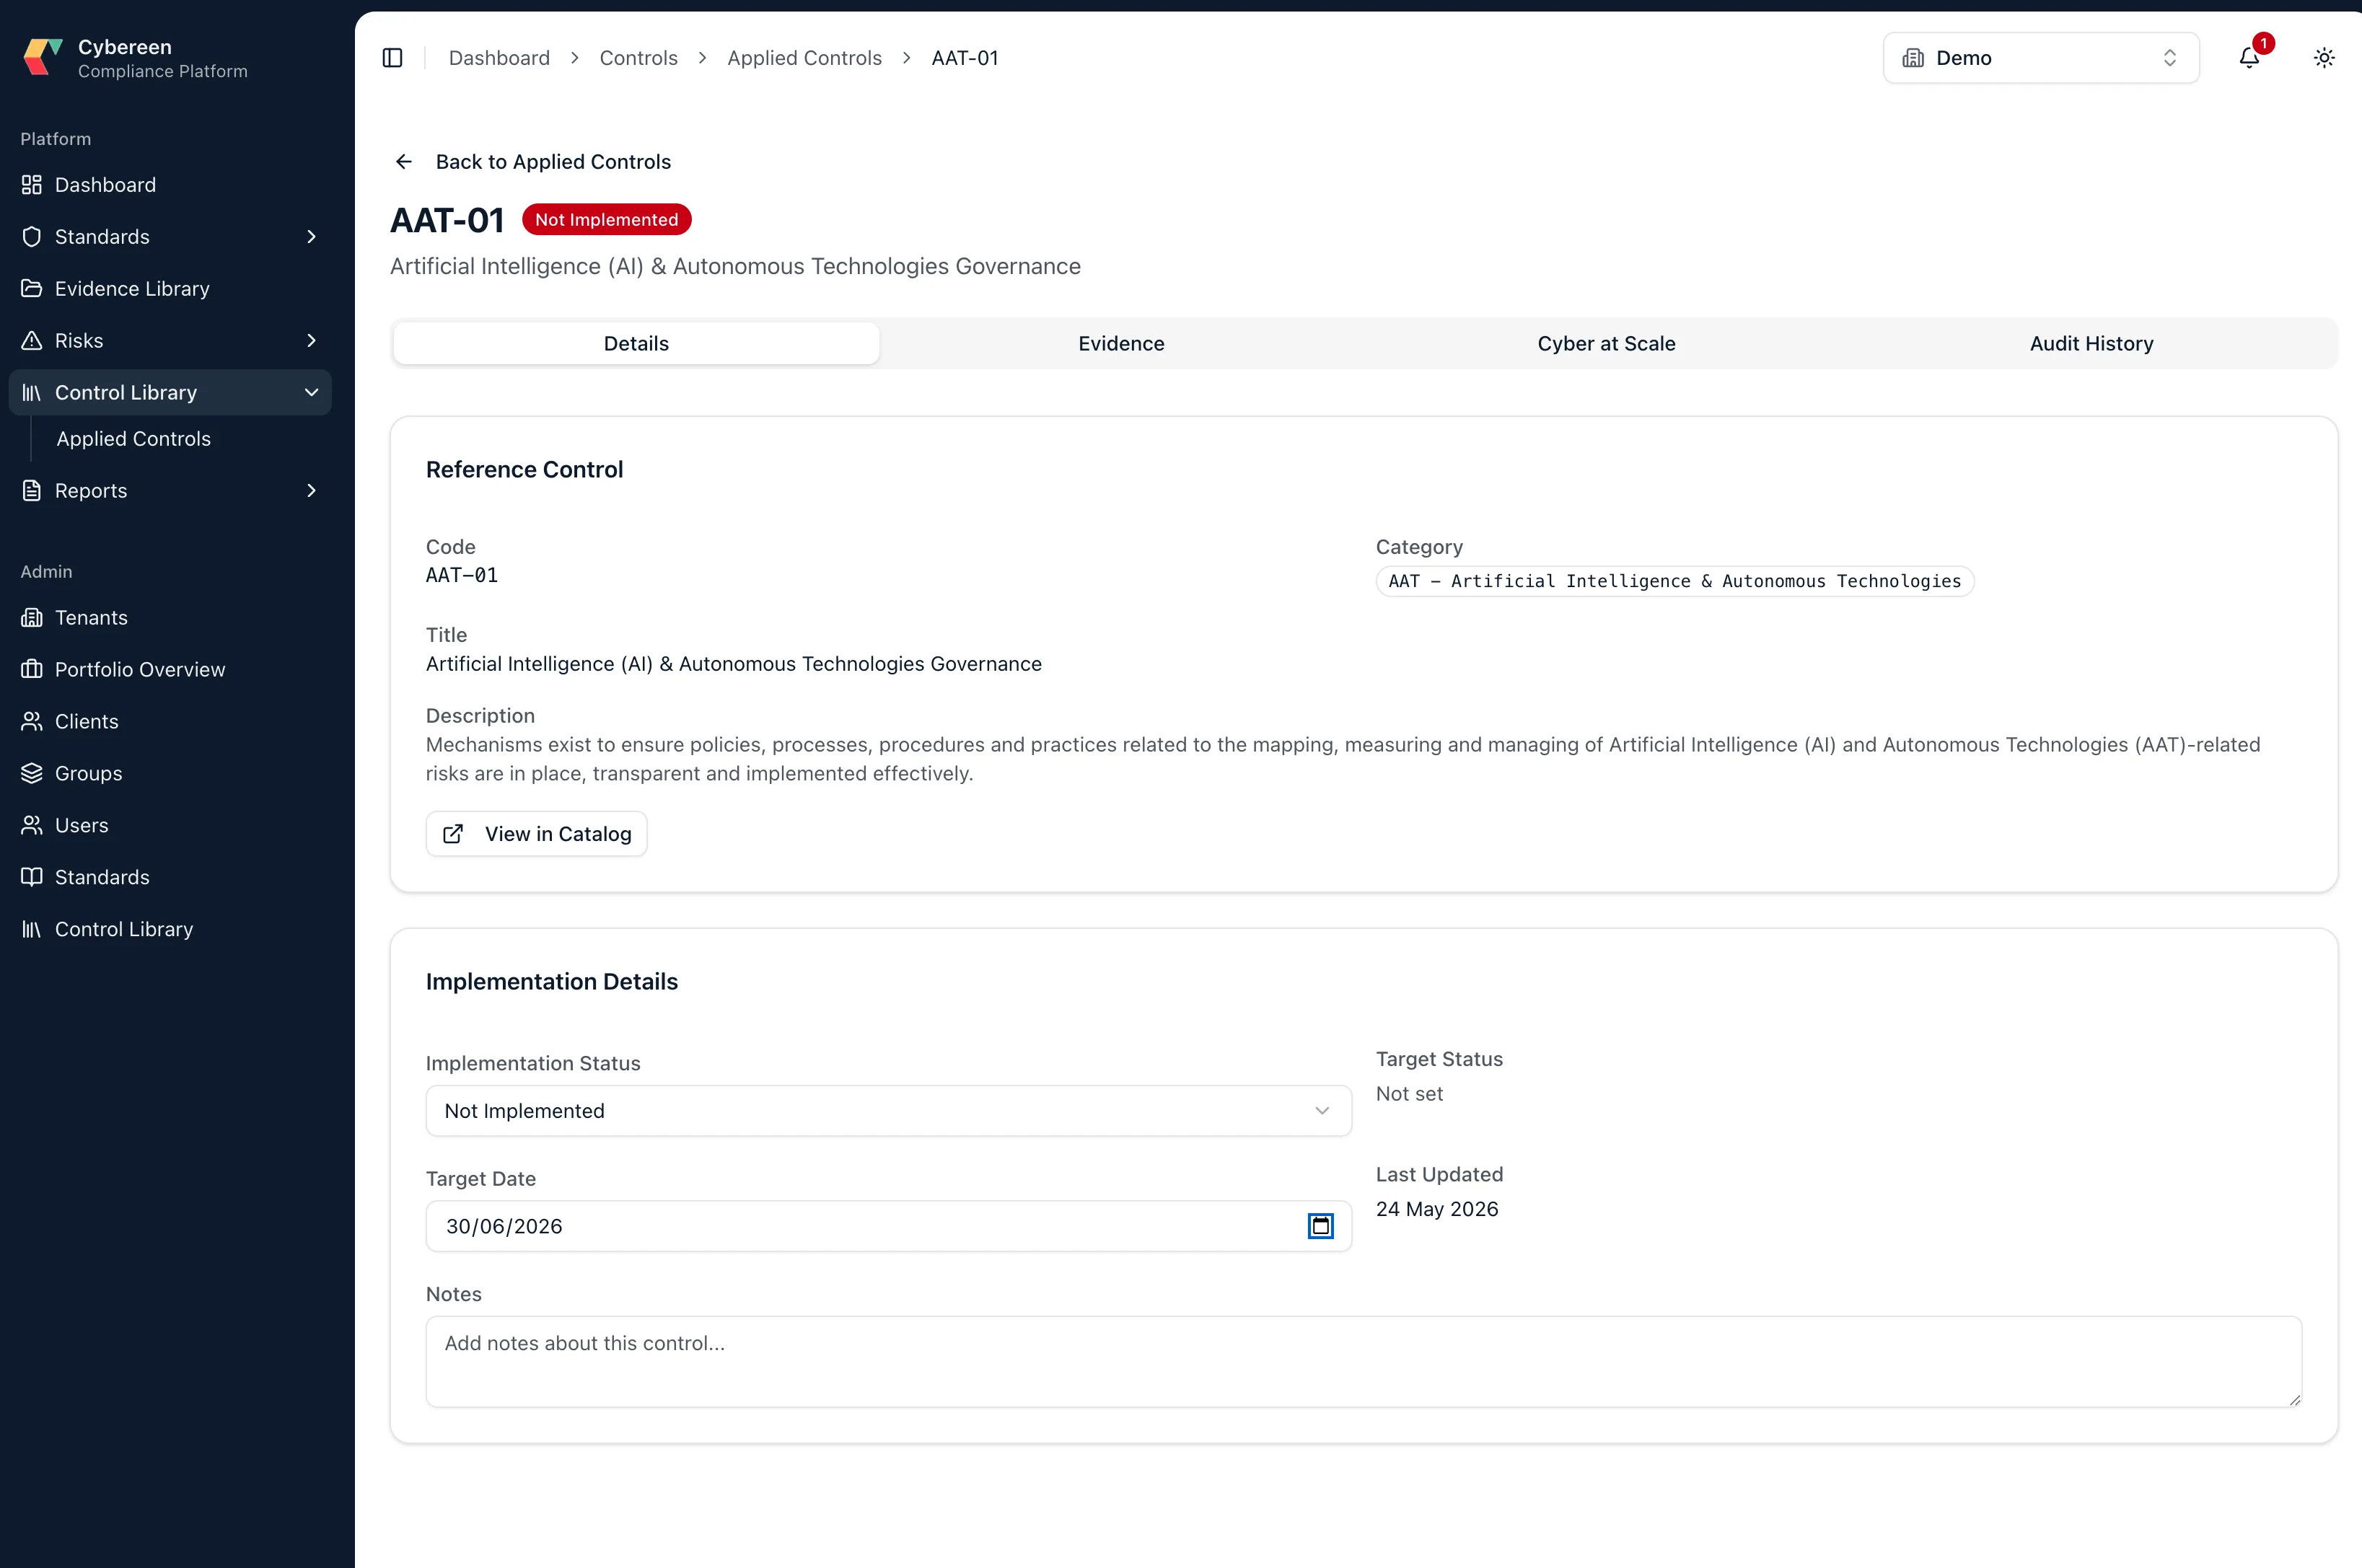
Cybereen v2.0 is here. Now control-driven.
Every requirement now maps to a single, reusable control - assess it, evidence it, and track it once, then watch it count across every standard. Plus multi-business-unit assessments, a redesigned UI, and AI-native foundations. Migration opens June 2026.
Explore the new platform →Built for the messy middle.
Spreadsheets + SharePoint
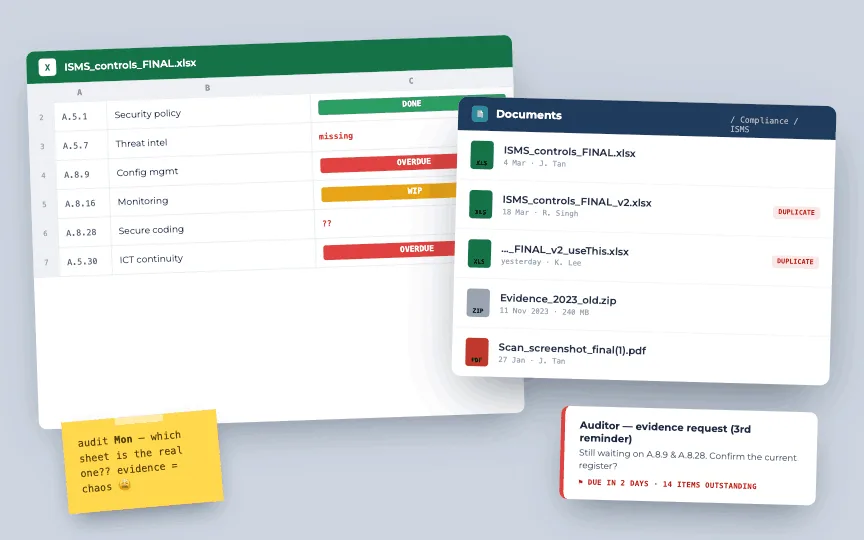
Versions diverge. Evidence scatters. Audits eat weeks. The board squints.
The middle that fits.
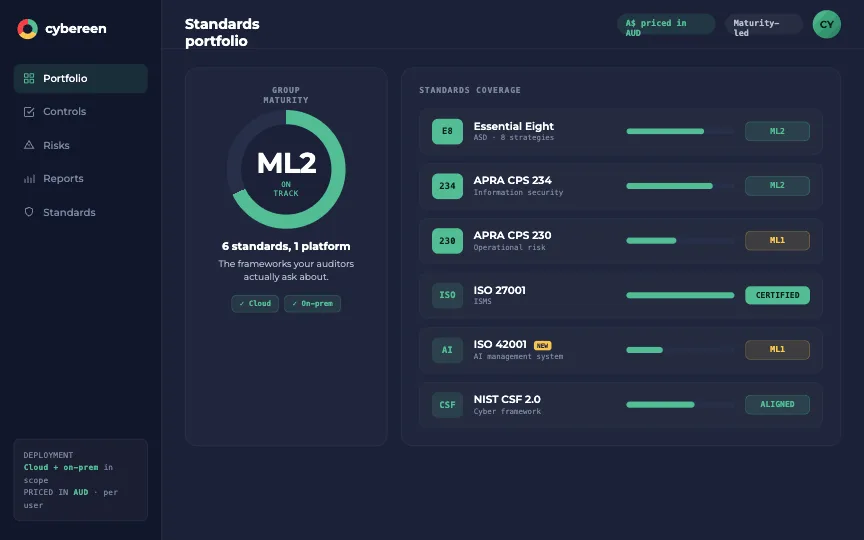
Built for the standards your auditors actually ask about. Per-user, far more affordable. Maturity-led.
Vanta · Drata · Sprinto
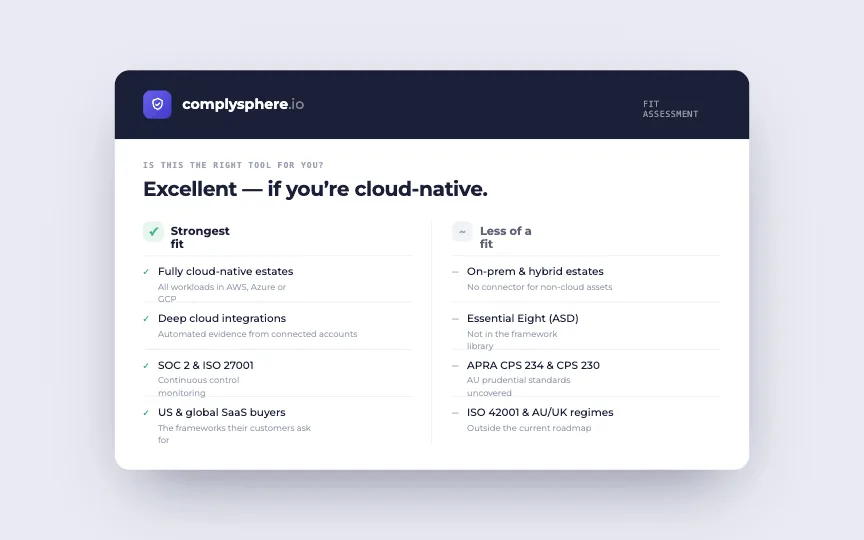
Excellent tools - strongest when you're cloud-native, with deep integrations into AWS, Azure and GCP. Less of a fit if you're not fully in the cloud, or held to AU/UK frameworks like Essential 8 and APRA.
Questions we hear every week.
Short answers. If you need deeper detail, the standards pillar pages go further.
What happens in the first week?
How do I get my spreadsheets into Cybereen?
Does one piece of evidence really count across multiple standards?
What do my board and my auditor actually receive?
How much work is it to keep current between audits?
Can I run multiple business units or client tenants?
How does pricing work?
How does Cybereen differ from Vanta or Drata?
Stop guessing. Start measuring.
See how Cybereen takes you from red to green across the standards your auditors actually ask about.